数字签名:信是谁发的,有没有被改Digital Signature: Origin and Integrity
活动通知被改成了另一个集合时间。小禾需要一种办法,让同学能发现改动,还能核对签名者。Someone changes the meeting time. He wants classmates to detect edits and check the signer.
第 1 步:不是贴一张手写签名图Step 1: More than a signature picture
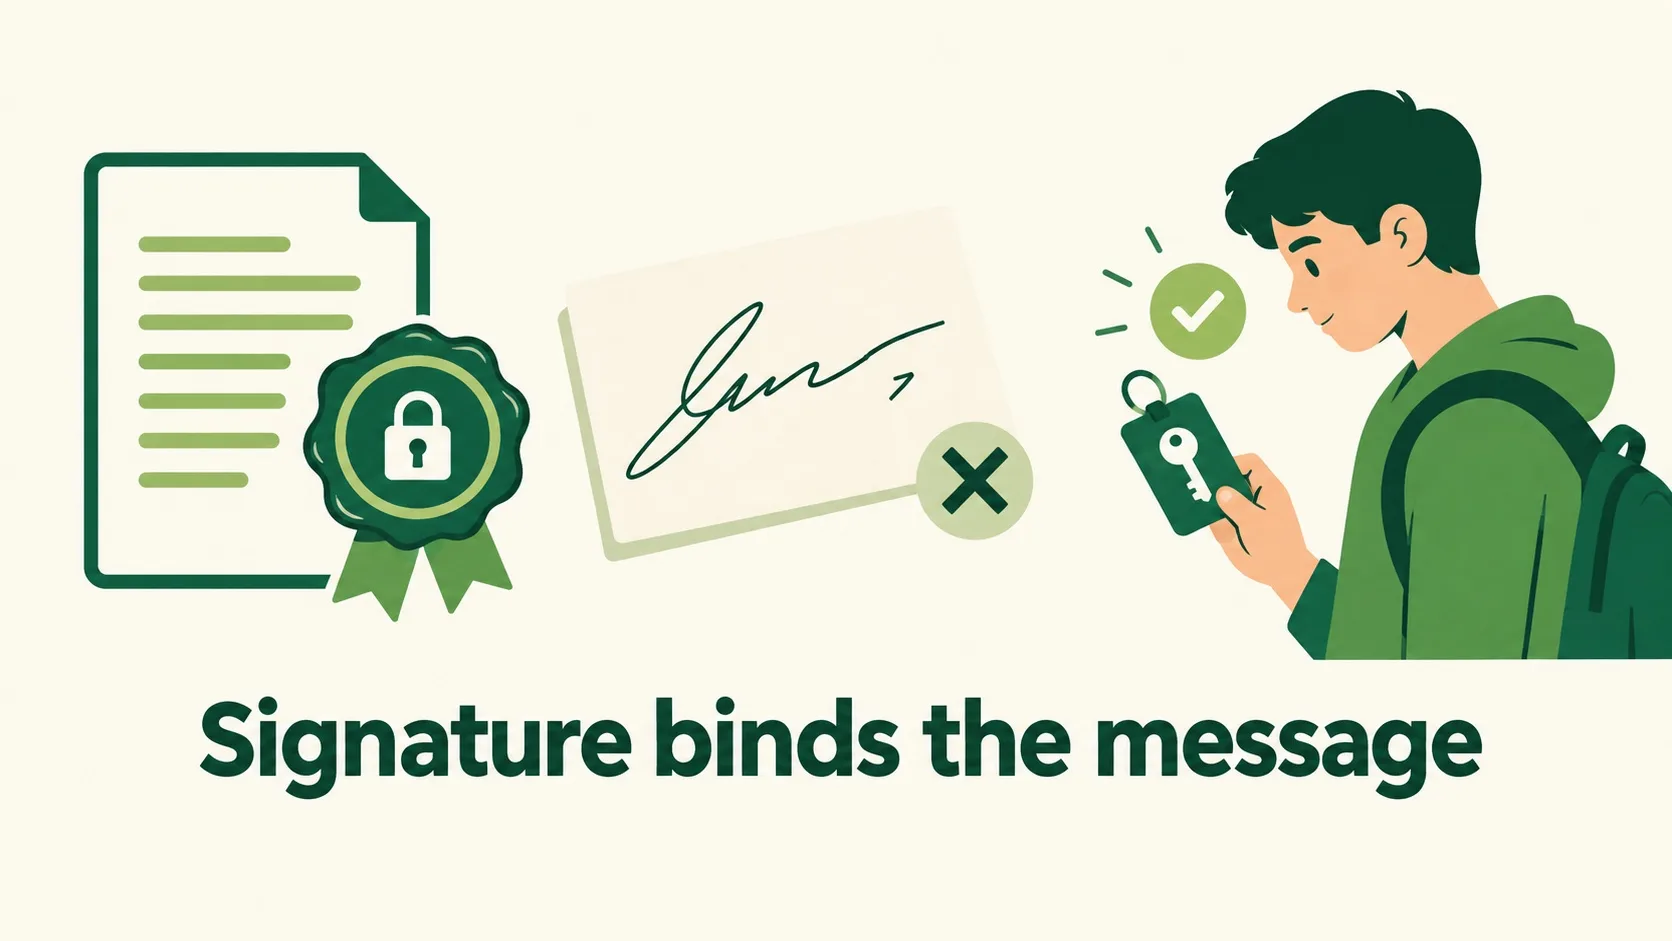
复制一张签名图片太容易了。A picture of a handwritten signature is easy to copy.
数字签名是密码学计算结果。签名者用私钥生成签名,验证者用对应公钥验证。签名与消息有关,改消息通常会使验证失败。它能帮助确认签名来源和完整性。但它不自动证明签名者所说的话是真的,也不自动让消息保密。A digital signature is a cryptographic result generated with a private key and checked with the corresponding public key. It is tied to the message, so changing the message normally invalidates it. It helps establish origin and integrity. It does not automatically make a statement true or hide the message.
第 2 步:公钥也要认对人Step 2: Know whose public key it is
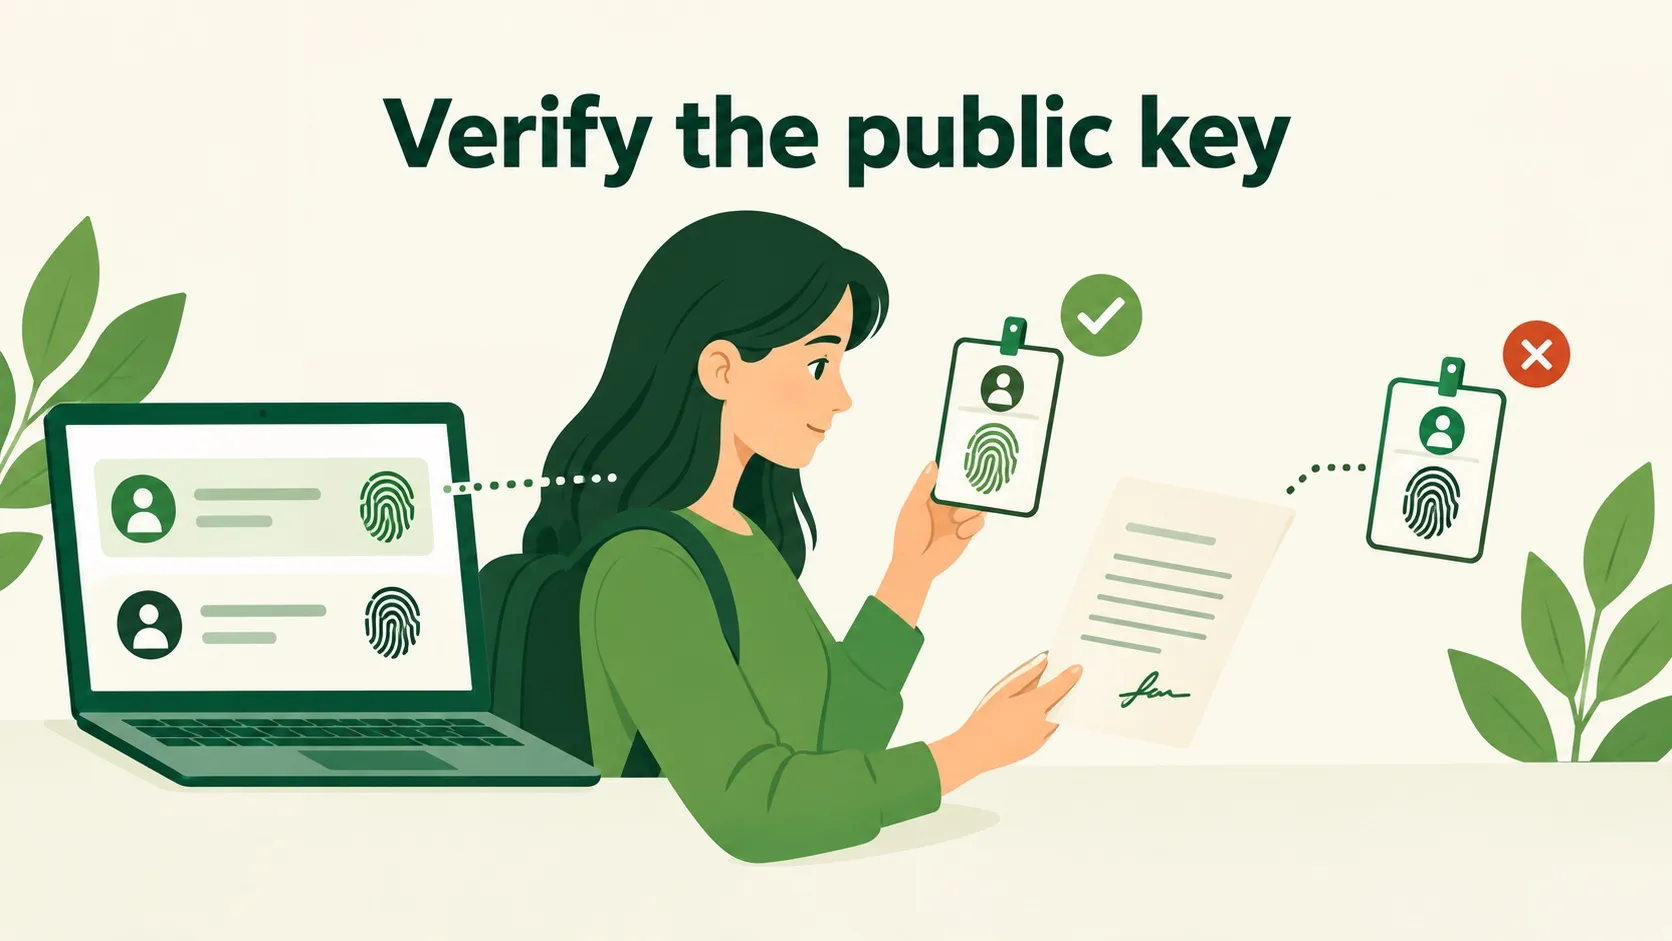
拿到一个公钥,就能认定身份吗?Does any supplied public key establish identity?
骗子也能生成自己的密钥对。验证通过,只能说明消息对应这把公钥。还需可信方式把公钥与身份关联。证书和经过核对的指纹可参与这个过程。私钥一旦泄露,别人可能冒充签名。身份关联和密钥管理,不能被一个绿色对勾替代。An impostor can generate a key pair too. A valid result establishes a relation to that key, not automatically to a real-world identity. Trusted key distribution, certificates or checked fingerprints can help establish the association. A stolen private key can enable impersonation. One green tick cannot replace identity and key management.
第 3 步:改字,再验一次Step 3: Edit and verify again
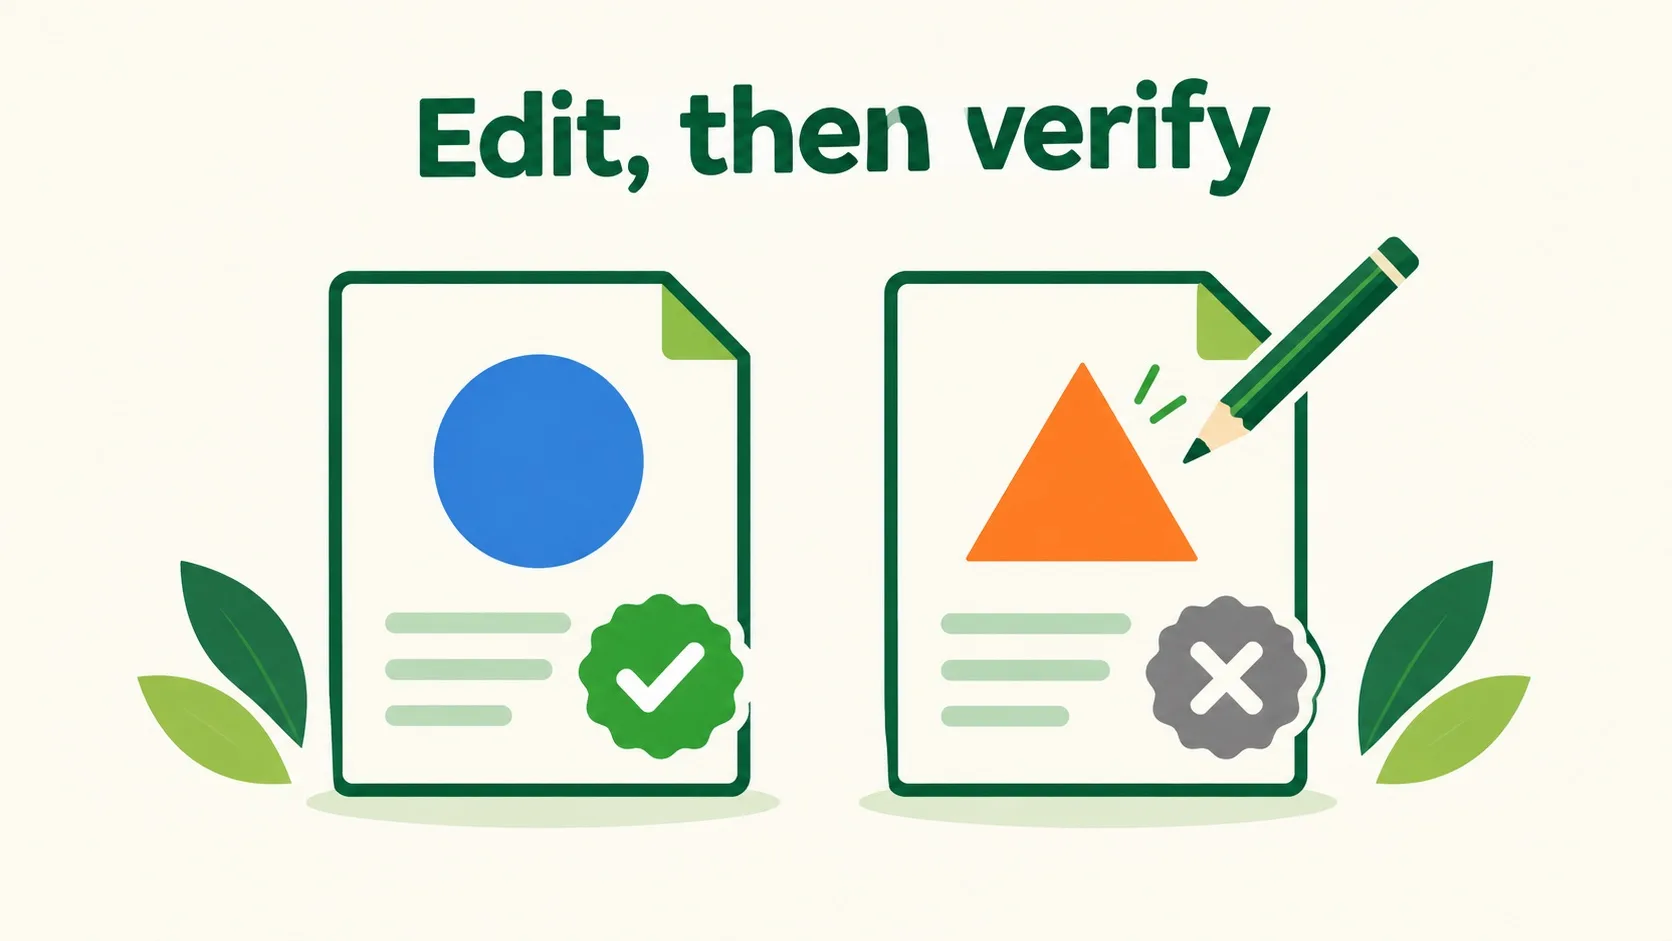
只改一个字会发生什么?What happens if one character changes?
小禾签好“九点集合”,随后把消息改成“十点集合”。原签名通常就无法通过验证。要发新消息,应对新内容重新签名。下面在浏览器生成临时密钥,真实执行签名和验证。密钥只用于本次演示,没有证书,不代表任何真实身份。He signs “meet at nine” and then changes it to “meet at ten.” The original signature should no longer verify. A revised message needs a new signature. The activity generates temporary keys in the browser and performs real signing and verification. These keys have no certificates and represent no real identity.
🎮 通知验签实验🎮 Notice signature experiment
依次尝试原文、篡改、换公钥与重新签名,比较真实验签结果。Try the original, a modified message, a different public key and a new signature. Compare actual verification results.
一句话记住它:Remember: 数字签名验证消息与密钥的关系,身份还需可信关联。A signature verifies a message–key relationship; identity needs a trusted association.
签名不等于加密。Signing is not encryption.改动消息会影响验签。Changing a message affects verification.公钥与身份的联系也要核验。The link between a public key and identity must be checked.
把握度:基本用途较高。演示使用临时 ECDSA 密钥,不提供证书或法律效力认定。Confidence: high for basic uses. The demonstration uses temporary ECDSA keys and makes no certificate or legal-validity claim.
AI 辅助制作与资料核对。插图和互动为教学示意。AI-assisted production and source checking. Illustrations and interactions are teaching models.
 Back to tree